Key Points
- The term “economic security” appears in the Corporate Governance Code for the first time, and the Code makes clear that addressing it is not only a matter of risk management but can also lead to revenue opportunities.
- Rather than treating economic security as a mere formal “checklist item,” the board of directors should treat it as a structural change in the company’s external environment and oversee how that change is reflected in management decisions.
- The challenge ahead is to connect the response to economic security not only to risk management but to corporate strategy and to the allocation of management resources—that is, where to direct resources such as people and capital.
In July 2026, the third revised version of Japan’s Corporate Governance Code was published. Building on the achievements and challenges of a decade of corporate governance reform in Japan, the revision seeks to advance that reform to the next stage. (I discussed the achievements and challenges of the past decade or so in the DCER Business Insight article “Corporate Governance in the Age of Economic Security,” published on February 25, 2026.)
This article focuses on economic security, which was explicitly incorporated into the Code for the first time in the 2026 revision, and considers its significance. It then examines what is required of boards of directors and outside directors, and what issues should be taken up going forward.
What It Means to Add “Economic Security” to the Revised Code
The Corporate Governance Code (hereafter, the “Code”) sets out the basic principles for the governance of listed companies. It is not a uniform, legally binding regulation but a framework that encourages each company’s autonomous response. Since its establishment in 2015, the Code has significantly influenced corporate management practices, including the role of the board, capital policy, and dialogue with shareholders and investors. This revision is the third, following those of 2018 and 2021.
Among the main features of this revision is an emphasis not only on capital efficiency but also on growth investment and the allocation of management resources. In addition, by narrowing the number of principles and newly establishing “interpretive guidelines” that supplement the thinking behind each principle, the revision reinforced a “principles-based approach” in which each company judges for itself in light of the principles, rather than having detailed rules imposed uniformly. Furthermore, with respect to outside directors, it shifted the emphasis from advising management toward oversight. Overall, the revision shifts the emphasis from formal compliance toward substantive responses tailored to each company’s own management challenges.
Against this backdrop, economic security was made explicit in the Code for the first time. Principle 4-4 (Roles and Responsibilities of the Board III: Effective Oversight of Management and Directors ②) provides that the board should appropriately establish internal control and enterprise-wide risk management systems. Enterprise-wide risk management is a mechanism for identifying and addressing key risks across the company as a whole, rather than leaving their management to individual departments.
The interpretive guideline for this principle now indicates that responses to cybersecurity risk, to the risk of supply-chain disruption due to geopolitical factors such as changes in the international economic-security environment, and to the risk of the outflow of technology and other information may be among the matters to consider when establishing a risk-management system. It further makes explicit that such responses can also lead to revenue opportunities.
At first glance, this may appear to be no more than the addition of risk items to the interpretive guideline, rather than to the principle itself, with economic security presented merely as one example of a change in the external environment. Yet its significance is by no means small.
First, two debates that developed from different contexts—economic security and corporate governance—have been formally connected. Economic security is rooted in the national security context of a nation’s independence, security, and prosperity, as well as the “strategic autonomy” of avoiding excessive dependence on other countries. For this reason, companies may be called upon to respond in ways that cannot be captured by short-term economic rationality alone.
By contrast, corporate governance reform—which became institutionalized particularly after the Cold War—developed with a focus on how to enhance corporate value under the market discipline imposed by shareholders and investors through capital markets. The two have, until now, been discussed according to different logics and in different vocabularies.
The explicit inclusion of economic security in the Code signals that competition among states and shifts in the security environment are no longer an issue external to corporate governance, but a factor that directly shapes corporate value and management decisions.
Second, economic security has been positioned not as sustainability or a social issue in the broad sense, but within the context of the enterprise-wide risk management the board is to oversee. This raises questions such as whether the company has a clear grasp of its critical technologies and data, whether it is overly dependent on particular parts of its supply chain, and whether changes in export controls, sanctions, and investment regulations are reflected in management decisions. Overseeing management’s understanding of the external environment, as well as the decisions and risk management systems based on that understanding—including arrangements for alternative procurement and business continuity in an emergency—becomes an important responsibility of the board.
Third, responses to economic security have been connected not only to risk management but also to revenue opportunities. For example, diversifying supply chains and investing in alternative technologies carry short-term costs, but can enhance supply stability. Appropriately protecting critical technologies and data can also create a competitive advantage.
In other words, the Code now frames the response to economic security not merely as a cost of regulatory compliance, but as something that bears on future business opportunities and competitiveness.
In this revision, oversight through important decision-making, rather than advice to management, was clearly positioned as the central role of independent outside directors, who are independent of the company. Insofar as economic security directly affects corporate management, outside directors are called upon to understand what structural changes in the external environment mean for their company, and to question the assumptions presented by management.
On that basis, they need to oversee, from the standpoint of medium- to long-term corporate value, factors that cannot be captured by short-term profitability or capital efficiency alone—security, supply chains, technology outflow, and reputation. However, strengthening the oversight function must not make management overly risk-averse. Supporting management in taking the risks necessary for growth is also a role of outside directors, and the knowledge and experience this requires, as well as the criteria for their selection and the design of training, are likewise in question.
The Code’s Next Step from the Perspective of Economic Security
The significance of incorporating economic security into the Code is considerable, but looking across the Code as a whole, its positioning remains one consideration within enterprise-wide risk management. At this stage, with the revision only just finalized, it is first necessary to observe how it takes root in corporate practice. On that basis, there are also issues that warrant further discussion, using this revision as a starting point, before the next revision.
The first is the position of government as a stakeholder in the company’s broader environment. The Code defines corporate governance as a mechanism through which a listed company makes decisions taking into account “the needs and perspectives of shareholders and also customers, employees and local communities.” General Principle 2 (“Appropriate Cooperation with Stakeholders Other Than Shareholders”) likewise lists employees, customers, business partners, creditors, local communities, and the like, but does not explicitly mention the government.
Today, however, governments and administrative agencies are not only regulators but actors that directly affect corporate strategy—through subsidies, government procurement, export controls, investment screening, economic sanctions, and industrial and technology policy. Indeed, the Keidanren document “Toward Corporate Governance for Sustainable Growth,” submitted to the Cabinet Secretariat’s Subcommittee for Promoting Japan as a Leading Asset Management Center, for the Formulation of a New Strategy under the Japan Growth Strategy Council, explicitly identifies the government as one of the actors in the governance ecosystem surrounding companies and investors—that is, as one of the actors that underpin corporate governance.
Given this reality, there is room for the Code to address more explicitly the relationship between companies and the government, administrative agencies, and other public actors. Governments and administrative agencies not only exert significant influence on corporate activity but are themselves affected by it. Precisely because the relationship between companies and the government now directly affects management strategy and corporate value, explicitly addressing such public actors in a future revision may warrant consideration.
The second is to position “changes in the external environment” themselves more clearly as a premise for board oversight. The enterprise-wide risk management that current Principle 4-4 requires naturally presupposes an awareness of the external environment surrounding the company.
In periods of major upheaval, however, firms may be constrained by past successes and existing assumptions and fail to recognize structural change. In the future, a principle or interpretive guideline could articulate an approach such as “appropriately identifying and evaluating important changes in the company’s external environment, and establishing a forward-looking enterprise-wide risk management system.”
The third is how to connect economic security to corporate strategy rather than confining it to risk management. Principle 4-1 (Roles and Responsibilities of the Board I: Setting the Broad Direction of Corporate Strategy, etc.) positions, as roles of the board, not only setting the broad direction of corporate strategy but also growth investment, the allocation of management resources, and the business portfolio. The interpretive guideline, too, calls for recognizing diverse investment opportunities, including domestic and overseas investment and investment in intellectual property.
On the other hand, economic security is positioned in the current Code mainly within the context of enterprise-wide risk management, and its connection to corporate strategy is not yet explicit. Yet economic security today bears directly on the business portfolio and the allocation of management resources—choices of production sites and markets to enter, the ownership and management of critical technologies, the selection of partners, the sourcing of critical resources, and the location of R&D facilities.
Therefore, in a future revision of the Code, rather than writing in specific matters in a fixed manner, there is room to articulate an approach whereby, in considering management strategy and the business portfolio, companies assess—according to the materiality of these issues for each company—how the geopolitical environment, economic-security policy, supply-chain resilience, and the protection of critical technologies and intellectual property affect their competitive advantage and business opportunities.
Principle 4-4 has already taken a step in this direction by stating that the response to economic security can also lead to revenue opportunities. Whether this thinking can be extended, beyond risk management, to corporate strategy and growth investment will be the next issue.
So That Economic Security Does Not Become a New “Checklist Item”
As security-related demands grow in importance, companies need to treat them not as constraints imposed from outside, but as structural changes in their own operating environment. On that basis, these changes must be connected to risk management, corporate strategy, the allocation of management resources, and medium- to long-term corporate value.
The Code itself states that the way each principle is implemented differs according to the environment surrounding the company and the like. Changes in the economic security environment are also a test of how well corporate governance can capture such structural change and reflect it in management.
What is needed is not to add economic security as yet another checklist item and address it merely as a matter of formal compliance. The 2026 revision is a first step toward reconsidering economic security as part of corporate strategy and toward rethinking the shape of corporate governance.
*The views expressed in this article are solely those of the author and do not represent the views of any organization, including the institution with which the author is affiliated.
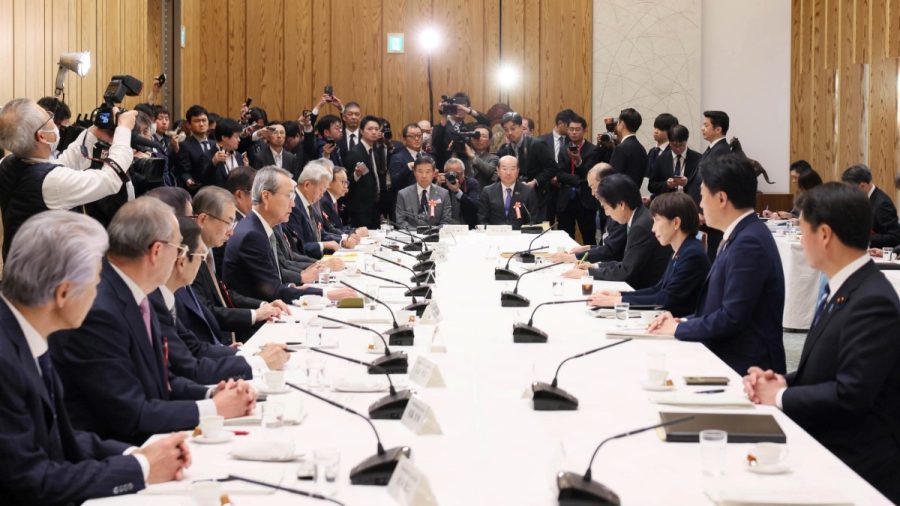
Source: “Meeting with the Japan Business Federation (Keidanren)” (Official Website of the Prime Minister’s Office of Japan), edited by DCER